

Meta representatives have indicated that the social media giant may need to “consider” withdrawing its encryption services from Canada if the government’s planned lawful access legislation is enacted without modifications.
The proposed Bill C-22 mandates that technology companies modify their systems to ensure they can provide information to law enforcement when requested with a warrant.
Currently under review in the Senate, Meta’s representatives expressed concerns that the bill exposes encrypted data—intended solely for the users who share it—to potential threats from malicious parties.
“In the end, the Canadian government would be enforcing a law that is not technically possible to comply with while still providing secure, end-to-end encrypted services to Canadians,” stated Robyn Greene, Meta’s director of privacy and public policy, during a session with the national security committee on Monday night.
Meta’s offerings encompass Facebook, Instagram, and the secure messaging platform WhatsApp.
When questioned about whether the legislation could result in the company removing some services from Canada, Rachel Curran, Meta’s head of public policy for Canada, mentioned that the organization would need to “evaluate all of our options.”
However, she acknowledged that it is a scenario the company would need to “consider.”
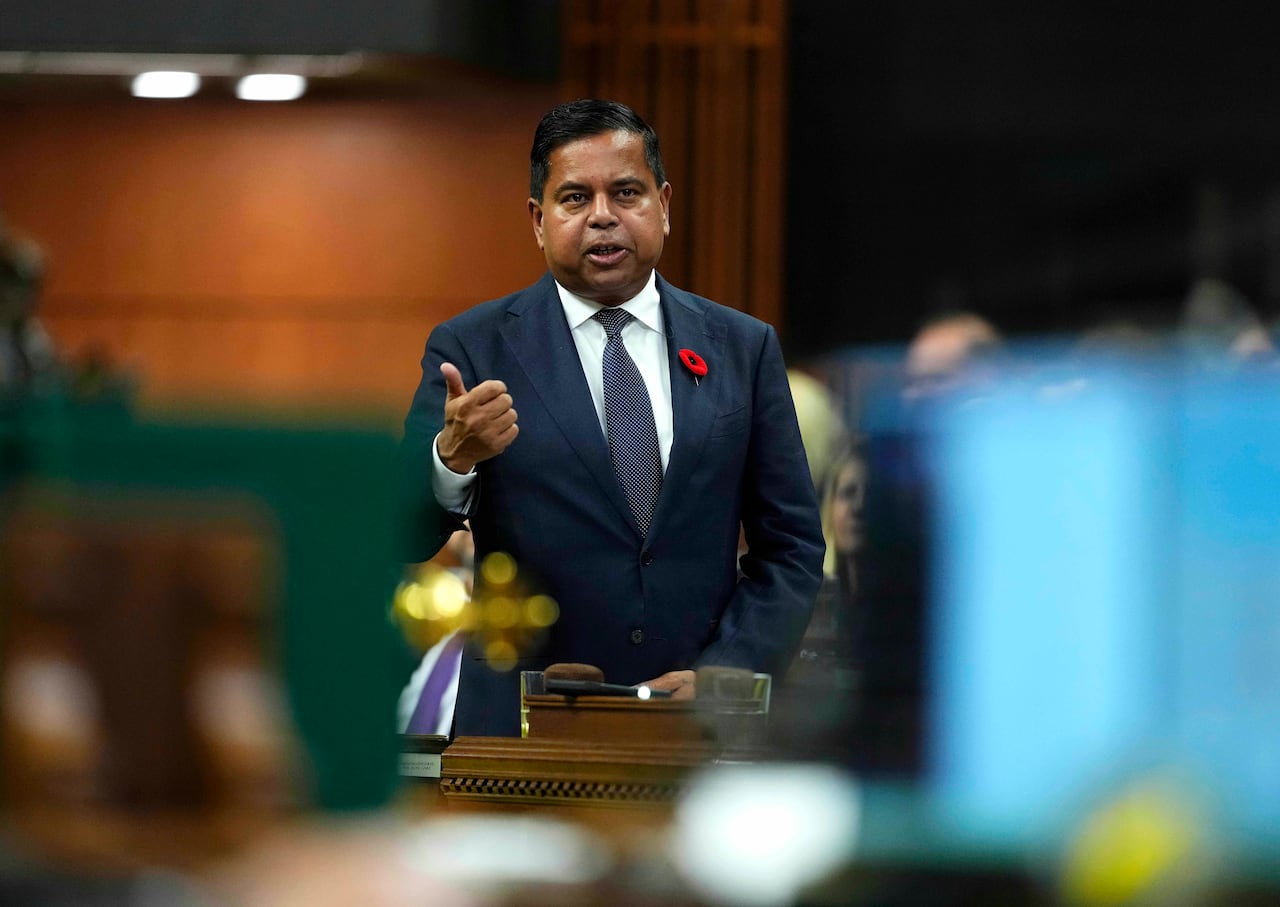
Minister of Public Safety Gary Anandasangaree proposed amendments to the lawful access legislation, but critics argue they don’t go far enough. (Justin Tang/The Canadian Press)
Bill C-22 also empowers the minister to issue confidential orders to electronic service providers (ESPs) in Canada, mandating them to incorporate surveillance and monitoring functionalities into their systems. Such orders would first undergo evaluation by the intelligence commissioner — an independent quasi-judicial figure.
Prior to the bill’s passage to the Senate in June, Public Safety Minister Gary Anandasangaree introduced amendments that imposed restrictions on the circumstances under which companies would be obligated to decrypt data.
Additionally, one amendment shortens the duration for which tech companies must retain metadata from a potential year to six months, following warnings from cybersecurity experts about the data being an enticing target for hackers.
Curran informed the Senate committee that the government’s amendments fall short of adequately safeguarding encrypted information.
“They have only protected the core, neglecting the outer layers that are essential to the encryption process,” she remarked.